Nearby attackers can crash Apple’s AirDrop before users see a file transfer request, temporarily disabling AirPlay, Handoff, Universal Clipboard, and other Continuity features. They’re no threat, assuming you’re configured properly.
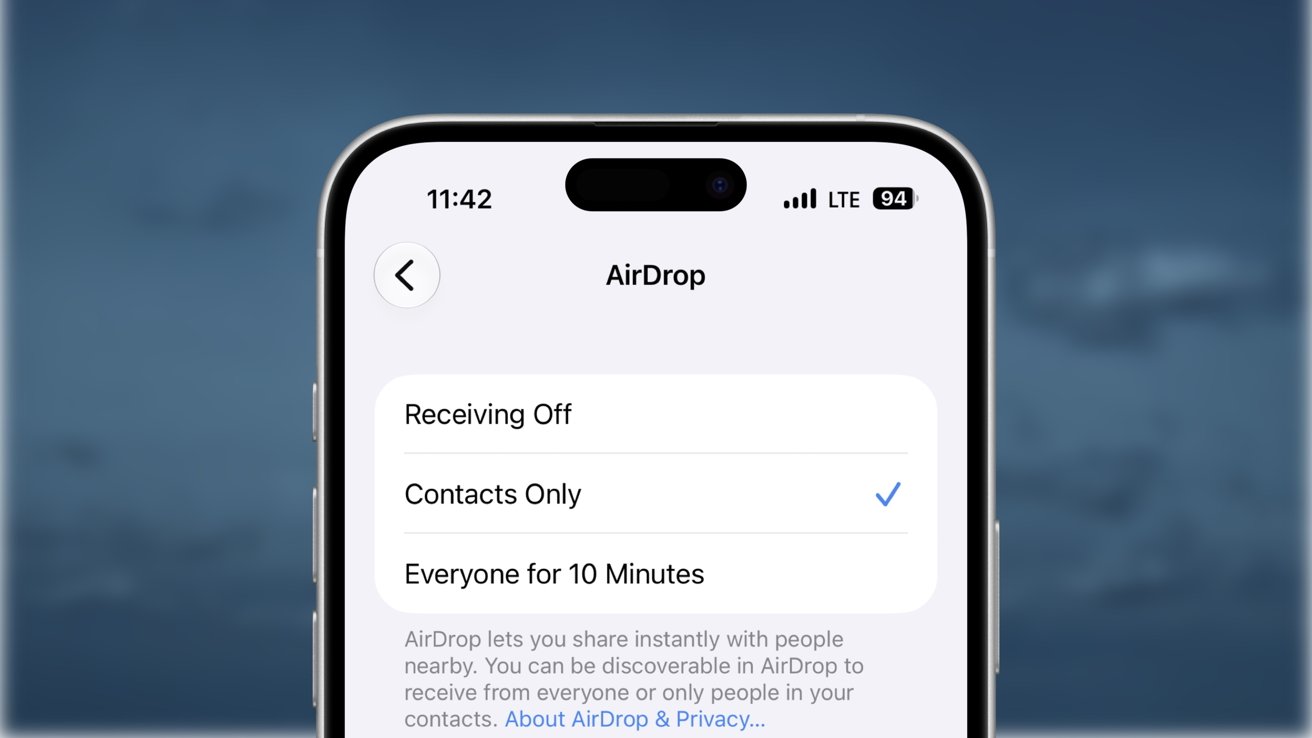 AirDrop settings on iPhone
The findings, published on June 30, also identify security flaws in Google and Samsung Quick Share. The CISPA Helmholtz Center for Information Security conducted the research.
Researchers Arash Ale Ebrahim and Nils Ole Tippenhauer analyzed the network protocols behind AirDrop and Quick Share. Their research identified three vulnerabilities affecting Apple’s AirDrop implementation.
The team also found three additional vulnerabilities affecting Quick Share on Android and Windows. These attacks require an attacker to be within wireless range of a target device, typically between 10 and 30 meters, without prior pairing, an existing contact relationship, or a shared Wi-Fi network.